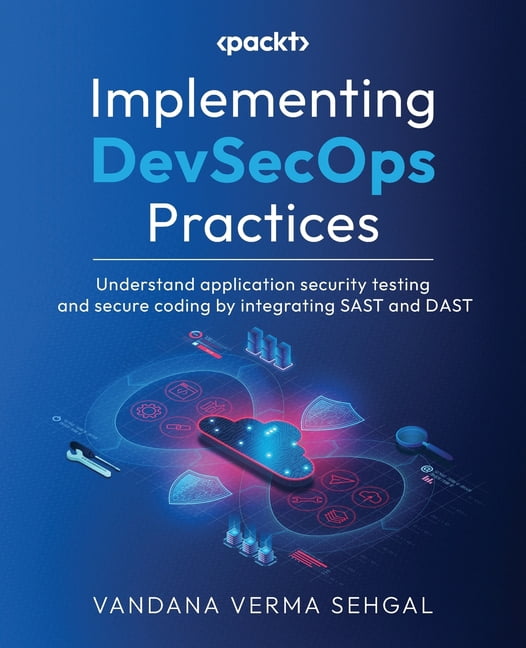


Implementing DevSecOps Practices: Understand application security testing and secure coding by integrating SAST and DAST, (Paperback)
 USA mağazasından ithal edildi

Ubuy, güvenliğiniz ve gizliliğiniz için yoğun çaba sarf etmektedir. Gelişmiş ödeme güvenlik sistemimiz, iletim sırasında bilgilerinizi AES (Gelişmiş Şifreleme Standartları) ve SSL (Güvenli Soket Katmanı) protokolleri kullanarak şifreleyerek gizliliği sağlar. Ödeme bilgileriniz, üçüncü taraf satıcılarla paylaşılmadığı için %100 güvende.


Hızlı
Kargo

Ücretsiz
İade*

Güvenli Paketleme

%100 Orijinal Ürünler

PCI DSS Uyumlu

ISO 27001 Sertifikalı


Ürün Detayları
- Integrate Shift-Left Security, automation, IaC, and compliance into every stage of development, ensuring strong application security and continuous protection for modern software with DevSecOps best practicesKey Features- Understand security posture management to maintain a resilient operational environment- Master DevOps security and blend it with software engineering to create robust security protocols- Adopt the left-shift approach to integrate early-stage security in DevSecOps- Purchase of the print or Kindle book includes a free PDF eBookBook DescriptionDevSecOps is built on the idea that everyone is responsible for security, with the goal of safely distributing security decisions at speed and scale to those who hold the highest level of context. This practice of integrating security into every stage of the development process helps improve both the security and overall quality of the software. This book will help you get to grips with DevSecOps and show you how to implement it, starting with a brief introduction to DevOps, DevSecOps, and their underlying principles.After understanding the principles, you'll dig deeper into different topics concerning application security and secure coding before learning about the secure development lifecycle and how to perform threat modeling properly. You'll also explore a range of tools available for these tasks, as well as best practices for developing secure code and embedding security and policy into your application. Finally, you'll look at automation and infrastructure security with a focus on continuous security testing, infrastructure as code (IaC), protecting DevOps tools, and learning about the software supply chain.By the end of this book, you'll know how to apply application security, safe coding, and DevSecOps practices in your development pipeline to create robust security protocols.What you will learn- Find out how DevSecOps unifies security and DevOps, bridging a significant cybersecurity gap- Discover how CI/CD pipelines can incorporate security checks for automatic vulnerability detection- Understand why threat modeling is indispensable for early vulnerability identification and action- Explore chaos engineering tests to monitor how systems perform in chaotic security scenarios- Find out how SAST pre-checks code and how DAST finds live-app vulnerabilities during runtime- Perform real-time monitoring via observability and its criticality for security managementWho this book is forThis book is for individuals new to DevSecOps and want to implement its practices successfully and efficiently. DevSecOps Engineers, Application Security Engineers, Developers, Pentesters, and Security Analysts will find plenty of useful information in this book. Prior knowledge of the software development process and programming logic is beneficial, but not mandatory.Table of Contents- Introducing DevSecOps- DevSecOps Principles
| Book format | Paperback |
| Fiction/nonfiction | Non-Fiction |
| Genre | Computing & Internet |
| Publication date | December, 2023 |
| Pages | 258 |
| Subgenre | Internet |
| Series title | No Series |
| Edition | 1 |
| Publisher | Packt Publishing |
| Original languages | English |
| Language | English |
| Edu focus | Engineering |
| Is collectible | N |
| Digital file format | |
| Digital reader format | |
| Digital audio file format | |
| Recording time | 0 min |
| Retail packaging | Single Piece |
| Assembled product dimensions (l x w x h) | 7.50 x 0.54 x 9.25 in (19.1 x 1.4 x 23.5 cm) |
| Assembled product weight | 0.99 lb (450 grams) |
| Bisac subject heading | Computers |
ÜRÜN AÇIKLAMASI
Implementing DevSecOps Practices: Understand application security testing and secure coding by integrating SAST and DAST, (Paperback)
Önemli bilgi
- Sınırlamalar : Uluslararası olarak gönderilen ürünler için, üretici garantisinin geçerli olmayabileceğini lütfen unutmayın; üretici servis seçenekleri mevcut olmayabilir; ürün kılavuzları, talimatlar ve güvenlik uyarıları hedef ülke dillerinde olmayabilir; ürünler (ve beraberindeki malzemeler) varış ülkesi standartlarına, spesifikasyonlarına ve etiketleme gerekliliklerine uygun olarak tasarlanmayabilir; ve ürünler hedef ülke voltajına ve diğer elektrik standartlarına uygun olmayabilir (uygunsa bir adaptör veya dönüştürücü kullanılmasını gerektirir). Alıcı, ürünün yasal olarak hedef ülkeye ithal edilebildiğinden emin olmaktan sorumludur. Ubuy veya bağlı kuruluşlarından sipariş verirken, alıcı kayıtlı ithalatçıdır ve varış ülkesinin tüm yasa ve düzenlemelerine uymalıdır.
- Ubuy küresel bir arama motoru olduğundan, Ubuy'da listelenen tüm ürünler satılık değildir. Ürünler ihracat/ticaret düzenlemelerine tabidir.
Şu anda stokta yok.
Bu ürünün tekrar stokta olup olmayacağıını veya ne zaman olacağını bilmiyoruz.
Bu ürün ülkemde kısıtlı değil. (Bu ürün ülkenizde kısıtlı değilse lütfen yukarıdaki bağlantıya tıklayın, böylece ekibimiz inceleyecek ve izin verecektir).
PCI DSS uyumlu ve ISO 27001:2022 sertifikalı olup, her siparişte şifrelenmiş ödeme ve tam alıcı koruması sunar.
Ubuy Güvencesi
%100 orijinal ürünler, PCI DSS uyumlu ödeme güvenliği, ISO 27001 sertifikalı veri koruması, en hızlı sınır ötesi teslimat, ücretsiz iade * ve her siparişte güvenli paketleme ile kaygısız alışverişin keyfini çıkarın.